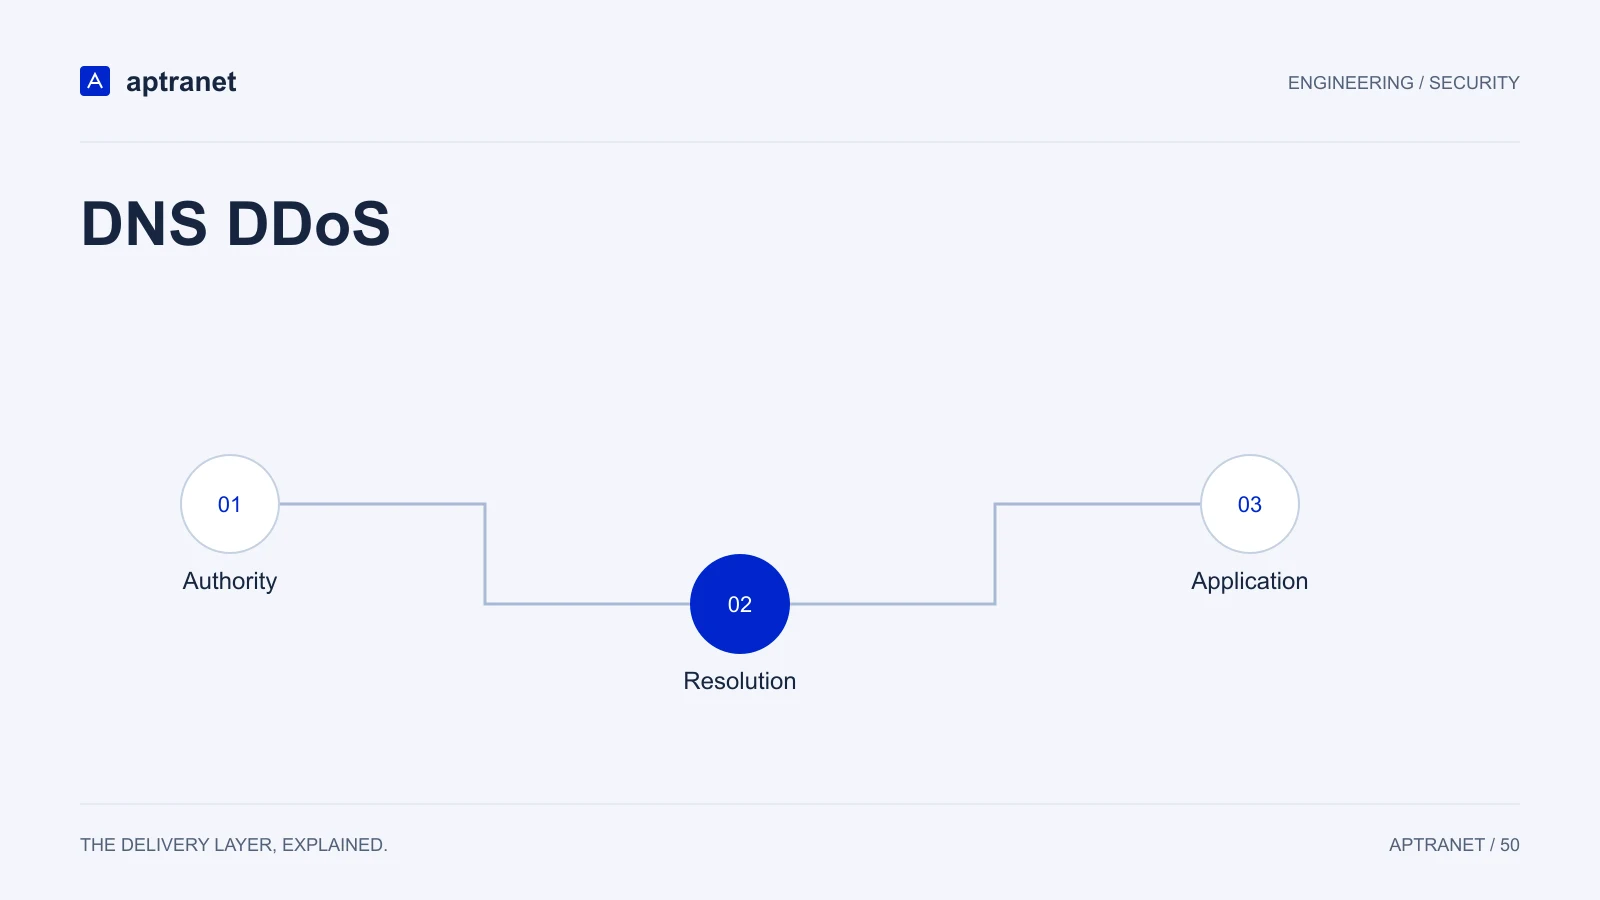
Authoritative DNS availability is a separate dependency from HTTP delivery. A protected website can still fail if its name cannot be resolved.
Small target, large blast radius
Authoritative DNS is a critical dependency even when HTTP delivery is protected. Review the DNS service distribution, capacity, mitigation scope, and escalation path.
The delivery model
DNS DDoS
- 01AuthorityKeep the authoritative service reachable.
- 02ResolutionResolvers obtain or reuse valid answers.
- 03ApplicationClients connect after resolving the name.
Anycast is the absorber
Anycast can distribute authoritative query traffic among serving locations. Routing, available capacity, filtering, and provider operations determine how the service behaves during an attack.
CDN plus DNS
HTTP floods hit Cloud CDN. DNS floods hit Cloud DNS. Use both when the hostname matters.
Validate before production
Monitor authoritative response rate and latency from independent locations. Review network diversity and the provider’s mitigation scope. Plan for registrar access, DNSSEC coordination, and incident communication without relying on the affected domain alone.
- Record the configuration and expected result before changing traffic.
- Keep evidence of the test and a working rollback for the previous behavior.