DDoS resilience depends on the protected traffic path, the attack type, and the capacity of every exposed dependency.
Volumetric versus application
L3-L4 floods fill pipes. L7 floods fill workers with expensive requests. The edge should take both. Origin Shield and cache also mean many L7 GETs never become origin GETs.
The delivery model
DDoS and CDN
- 01AbsorbHandle traffic at the appropriate network boundary.
- 02FilterApply controls suited to the request or attack type.
- 03PreserveKeep legitimate application and DNS paths available.
Hide then restrict
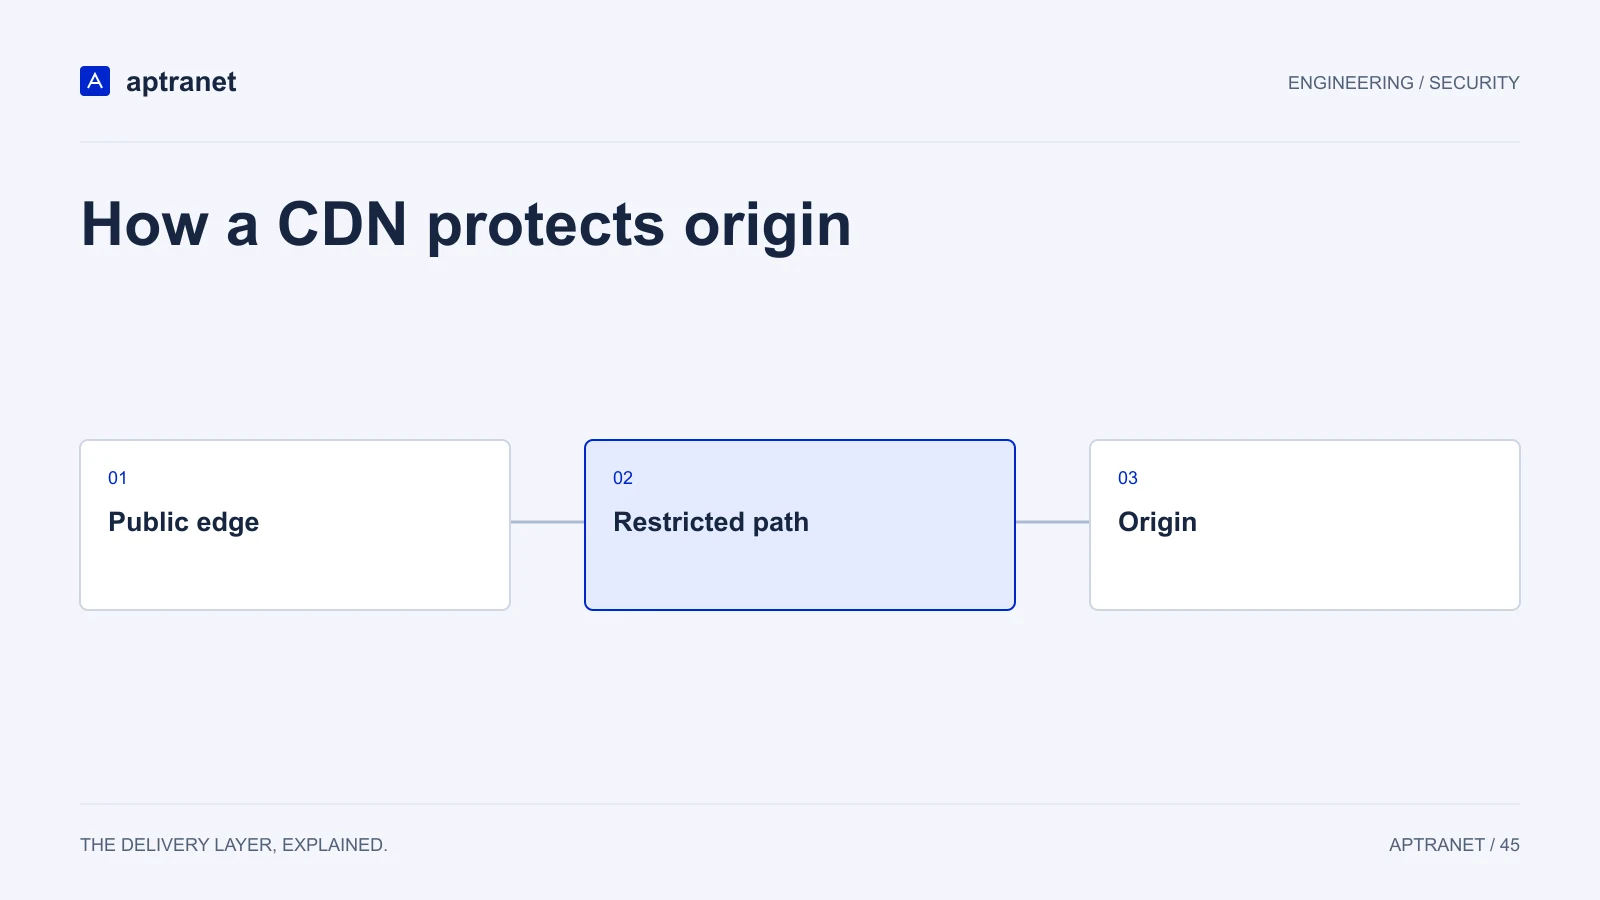
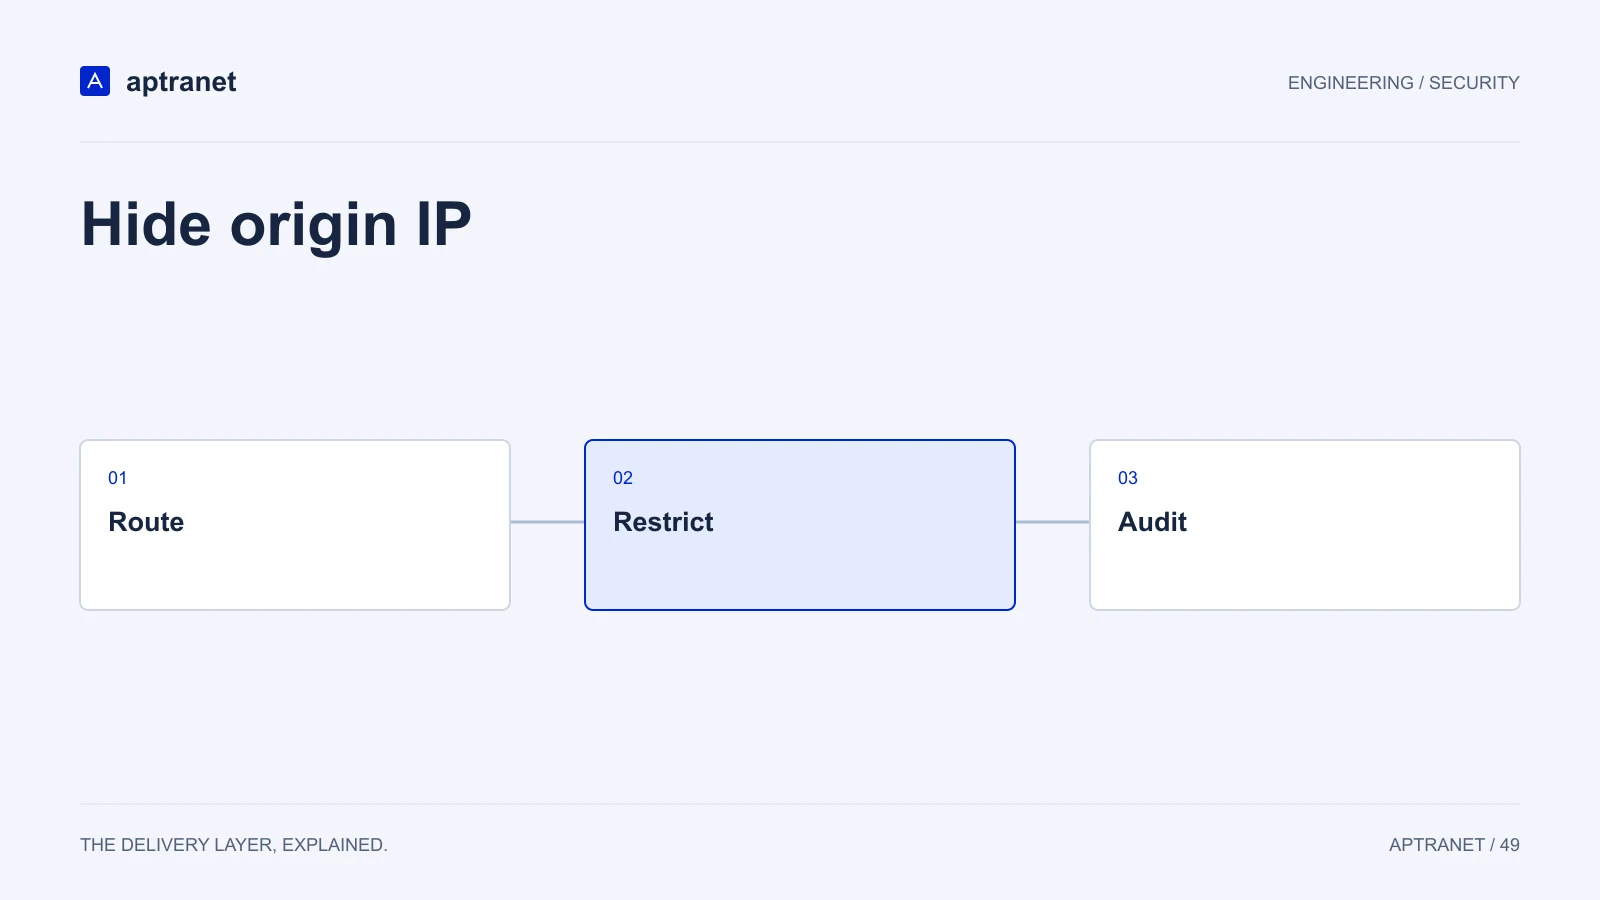
Cut over DNS, then firewall origin to pull paths only. An uncovered origin IP is a second public hostname you forgot.
DNS is a separate flood
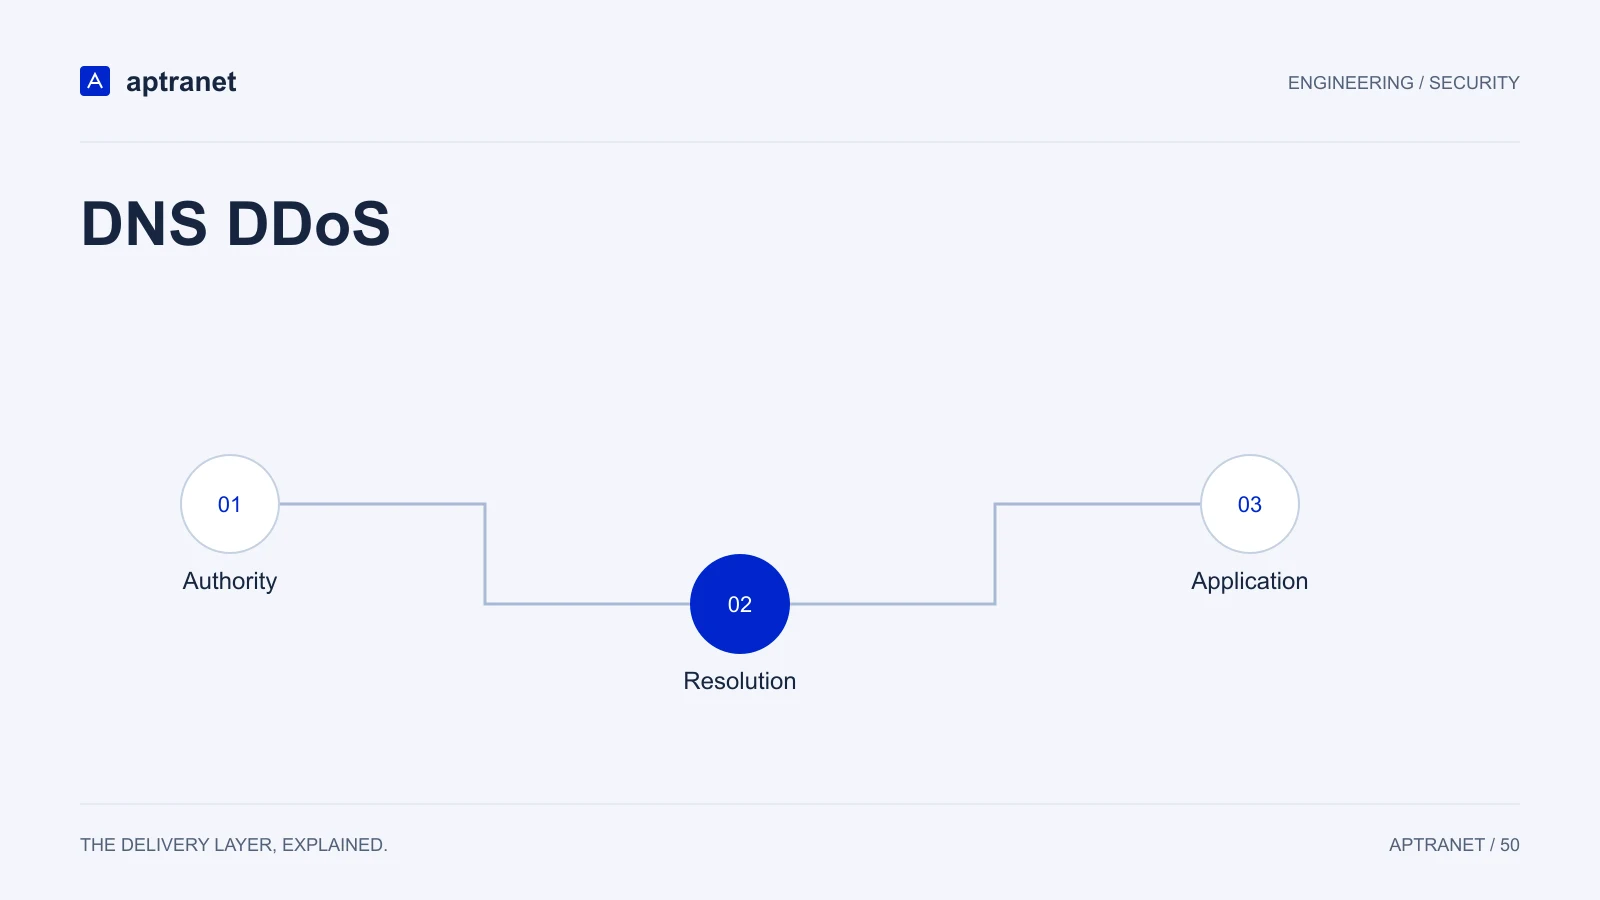
Authoritative Cloud DNS is DDoS-protected Anycast. Host the zone there if the name itself is the target.
Practice before you need the phone
Know the emergency page and the number. An active incident is a poor time to create a distribution from scratch.
Validate before production
Inventory public origins, DNS, APIs, and non-HTTP services before an incident. Review the provider’s protection scope and escalation process. Use an agreed, controlled resilience exercise rather than generating unsolicited attack traffic.
- Record the configuration and expected result before changing traffic.
- Keep evidence of the test and a working rollback for the previous behavior.