Signed delivery tokens need validation before cached content is released, with an expiry and scope appropriate to the resource.
Gate the hit
Authorization must be checked before releasing protected content, including on a cache hit. Confirm this behavior with warmed objects and invalid tokens rather than assuming the cache enforces it.
The delivery model
CDN token authentication
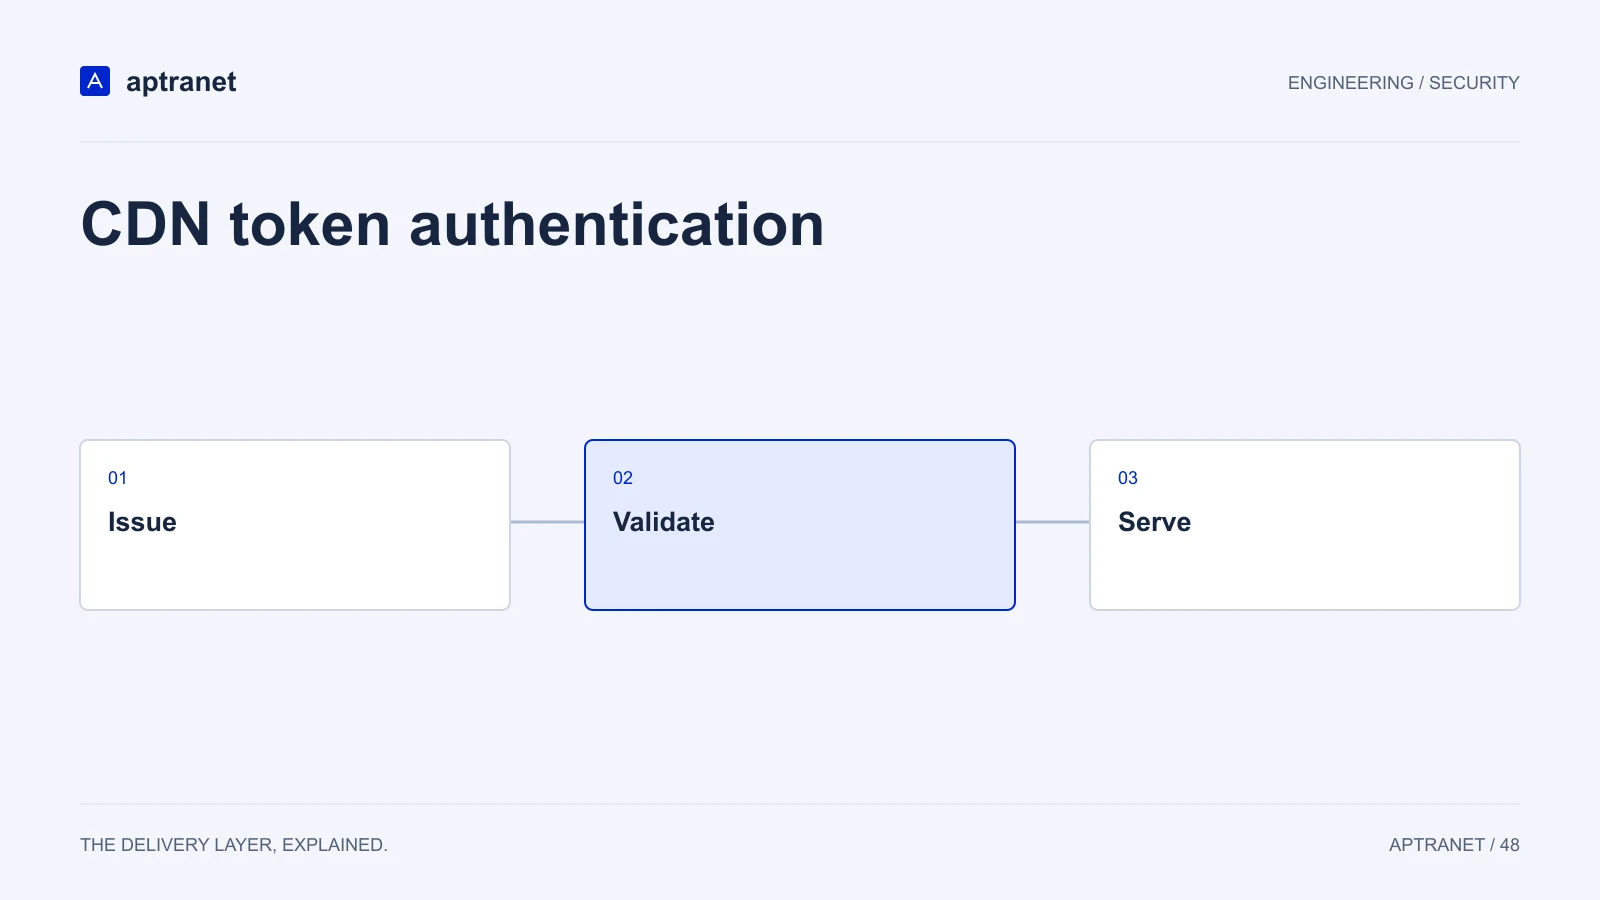
- 01IssueAn authorized application creates a scoped token.
- 02ValidateThe delivery layer checks signature and restrictions.
- 03ServeOnly an allowed request receives the cached object.
Expiry matches the product
Rental windows, pre-load windows and one-time downloads need different lifetimes. Short expiry limits leaked URL reuse.
Public and private on one distribution
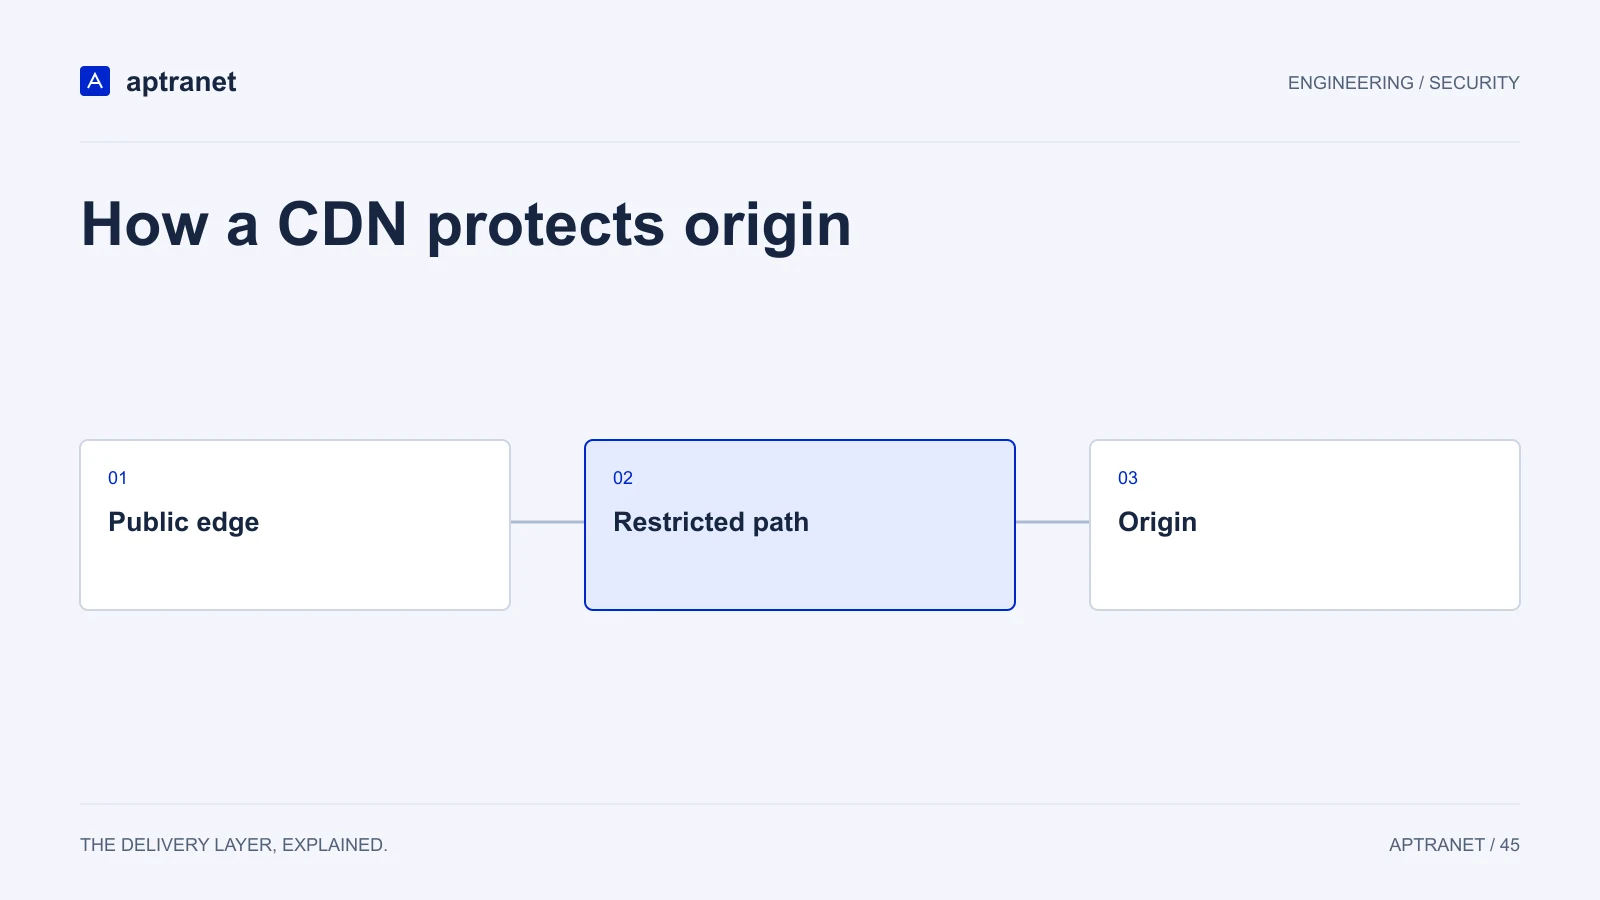
Marketing pages stay public. /downloads and /hls paths require tokens. Path policy, not a second CDN.
Not a replacement for login
The application still mints the URL after it checks entitlements. The CDN enforces the URL. Billing stays in the app.
Validate before production
Warm a protected object, then request it with valid, expired, missing, and modified tokens. All unauthorized cases must still fail on a cache hit. Test range requests and playback continuation near expiry.
- Record the configuration and expected result before changing traffic.
- Keep evidence of the test and a working rollback for the previous behavior.